PHP2Shell and “Black October”: what AI-found vulnerabilities mean for every language
AI models helped find two unauthenticated remote-code-execution flaws in PHP’s core engine, the runtime behind up to 70% of websites. Attacks began within minutes. What happened, why npm and PyPI face the same pressure, and what every team should change.
On 21 October 2026 the PHP project shipped emergency releases for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, nicknamed PHP2Shell. Both allow remote code execution without authentication, before a single line of application code runs. Wiz Research found them with the help of AI models. Within an hour of disclosure, Cloudflare reported tens of thousands of exploit attempts. This was not a bug in WordPress or a plugin: it was the engine underneath them.
What PHP2Shell actually is
CVE-2026-109618 is remote code execution through out-of-memory corruption; CVE-2026-109619 is remote code execution through stale global state. Both carry a CVSS v4.0 score of 9.2. Wiz demonstrated working exploits against WordPress, Drupal and Joomla, and setups using mod_php are the most exposed.
Because the bugs sit in the request-handling engine, a perfectly written application is still vulnerable. Code review, a WAF rule for SQL injection or a hardened admin panel do not help if the runtime itself can be taken over.
The timeline shows how long coordinated disclosure still takes: found on 19 August, reported on 24 August, acknowledged on 21 September, patched on 21 October.
# Fixed releases: 8.5.12, 8.4.27, 8.3.36, 8.2.35
php -v

# Stopgap from the PHP project while you patch (php.ini)
session.upload_progress.enabled = 0
Reference: PHP — security releases (21 October 2026) · Wiz Research — PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet
Why AI changes the maths
Memory-safety bugs in decades-old C code are not new. What is new is the speed. AI-assisted analysis let a small team go through an engine as large as PHP in weeks, and attackers have access to similar tools. The window between “patch published” and “exploited at scale” has shrunk from days to minutes.
The response showed it. The NSA advised operators who could not patch immediately to take sites offline temporarily, some sites went dark for a few hours, and news outlets started calling the month AI’s “Black October”.
The window between a patch being published and mass exploitation is now measured in minutes, not weeks.
Reference: Fortune — AI tools discovered the PHP vulnerability that could take down 70% of the internet · TidBITS — PHP2Shell vulnerabilities put 70% of websites at risk
Not just PHP: npm, PyPI and the AI supply chain
PHP2Shell is a runtime bug, but the same pressure is hitting package ecosystems. In May 2026 the “mini-shai-hulud” campaign pushed 404 malicious versions across more than 170 npm packages and 2 PyPI packages, including packages from TanStack, Mistral AI, UiPath and OpenSearch.
AI coding agents add new routes in. Slopsquatting is one: attackers register package names that models hallucinate and wait for an agent to install them. Another is agent config and instruction files committed to repositories, which can be used for persistence. JavaScript, Python and Rust (Cargo) teams face this risk as much as anyone running PHP.
Reference: SafeDep — Mass npm supply-chain attack hits TanStack and Mistral AI · Andrew Nesbitt — Package security problems for AI agents
A checklist for every team
Patch runtimes, not just apps. Track the PHP, Node.js, Python and OS versions behind every service, and decide who upgrades them. PHP 8.1 and older no longer get official fixes, and 8.2 reaches end of life on 31 December 2026.
Pin and review dependencies. Use lockfiles, install with npm ci or pip with hashes, wait a few days before adopting brand-new versions, and never let an AI agent add a package without a human checking that it exists and is the one intended.
Assume minutes, not days. Keep edge protection (Cloudflare or similar) in front of public services, keep backups off the server, and rehearse a “take it offline and patch” runbook.
| Risk | What to do this week |
|---|---|
| PHP below 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12 | Upgrade, or ask your host to confirm in writing |
| PHP 8.1 or older | Plan the move to a supported version now |
| New npm / PyPI dependencies | Lockfiles, hashes, a short cooldown, human review |
| AI agent installing packages | Check the package exists and is the intended one |
Where CodexPal stands
Our own products, including KhataIN, run on Python and TypeScript rather than PHP, so PHP2Shell does not affect them. The supply-chain lessons apply to us fully, and we treat them that way: pinned dependencies, reviewed upgrades and edge protection in front of every public service.
The takeaway
AI did not create PHP2Shell; the bugs were there for years. AI made them findable, by defenders and attackers alike. The teams that come through this best will be the ones that can patch a runtime the same day and know exactly what is in their dependency tree.
Sources & further reading
Primary references checked on October 24, 2026. Examples and diagrams are illustrative unless stated otherwise.
- PHP — security releases (21 October 2026)
- Wiz Research — PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet
- Fortune — AI tools discovered the PHP vulnerability that could take down 70% of the internet
- TidBITS — PHP2Shell vulnerabilities put 70% of websites at risk
- SafeDep — Mass npm supply-chain attack hits TanStack and Mistral AI
- Andrew Nesbitt — Package security problems for AI agents
More to think about.
How to prepare a .com.np domain application
Follow the official registry process, choose an appropriate name and keep the domain under the right owner’s control.
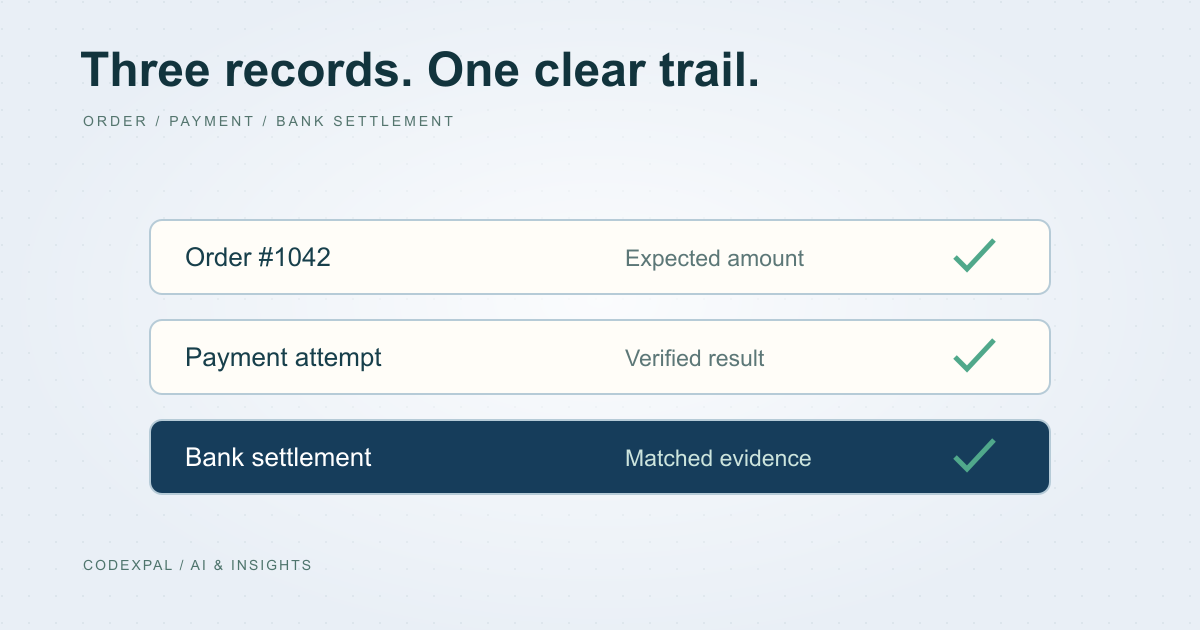
Design a secure payment reconciliation workflow
Separate orders, payment attempts and bank settlements so duplicate returns, delayed results and refunds remain explainable.